Claude Code v2.1.326 Release: Code Mode and Agent Teams
Anthropic released Claude Code v2.1.326 on November 16, 2026. Code Mode can now be turned on while agent teams are enabled, and terminal and VS Code sessions with no mode set start in auto mode instead of Manual mode when organization policy has not loaded. Sandboxed commands also stop writing to some sensitive home folders by default.
The startup default is the change most users will feel first. A session that opens before policy loads no longer waits in Manual mode by default. Once settings do load, the release notes say those sessions take a server-managed defaultMode, or Manual if settings fail with no stored copy and policy fails or requires it. In practice, the first minutes of a session can now run under a different permission posture than the one a team configured, which makes a quick check after updating worth doing.
Code Mode With Agent Teams
Code Mode, introduced as an experimental feature in v2.1.323, is the mode where Claude writes JavaScript that calls tools directly. Until this release, turning it on alongside agent teams was not supported. The v2.1.326 notes close that gap in one line: support for turning on Code Mode while agent teams are enabled, and if you already turned it on, sessions with teams on now start in Code Mode.
That matters because teams and Code Mode solve different halves of the same problem. Agent teams split work across parallel sessions, while Code Mode reduces the round trips inside one session by letting the model script its tool calls. Combining them means a multi-agent setup no longer has to give up the scripting layer. The release also fixes two Code Mode defects that would have made the combination unreliable: background subagents started in Code Mode no longer fail when they preload a skill with an inline shell command, and mods can again use Bash, Read and other tools through the Code Mode tool helpers.
Code Mode is still labelled experimental. This release widens where it can run, it does not promote it to a stable feature, and Anthropic gives no date for such a move. Teams adopting the combination should treat it as a capability to test on bounded work first, not as a new default for every session.
Auto Mode Startup Default
The changed section of the release notes states the new rule plainly: terminal and VS Code sessions with no mode set start in auto mode, not Manual mode, when the organization policy has not loaded. A related change applies to organizations with the Claude Code and Cowork HIPAA configuration, which also start in auto mode by default, with disableAutoMode available to turn it off. On a direct Anthropic API connection, the server-side classifier now checks actions for those HIPAA organizations, as it already did for other organizations.
The nuance is in what happens next. Sessions that start in auto by default take a server-managed defaultMode once settings load. If settings fail and there is no stored copy, they fall back to Manual when policy fails or requires it. So auto mode here is a bridge state for the policy loading window, not a permanent override of managed settings. Even so, a bridge state is still a state in which tool calls can run, and auto mode also changed in this release to stop some shell commands that ran before, while some Bash commands on macOS that ran before now ask or are refused.
My read: the risk is not that Anthropic removed Manual mode. The risk is surprise. A user who never picked a mode, and who expected the conservative default, now starts in the more permissive one for as long as policy takes to load. Teams with managed settings should verify what a fresh session shows in its first minute, rather than assuming the configured mode was in force from the start.
Sandbox Write Protection and Startup Warnings
Sandboxed commands on macOS, Linux and WSL no longer write to some sensitive home folders by default. Some of those folders can be allowed with sandbox.filesystem.allowWrite in user or managed settings. The release notes do not publish the full list of protected folders, so that list is unconfirmed here. The surrounding sandbox changes point the same way as v2.1.325, which made sandboxed Bash follow the normal permission flow: the sandbox keeps its state in some cases during a session until you run /sandbox or /cd, unexpected entries in a repository .git folder are set aside after a command, and commands rewritten by a permission hook or SDK host while approving stay in the sandbox if the original was checked as sandboxed.
Two smaller additions make misconfiguration easier to catch. Startup now warns when an --allowedTools, --disallowedTools or --tools value has an entry that does not look like a complete rule, which previously could fail silently. And /status gains a row that says when a provider or an environment variable such as DISABLE_TELEMETRY turns features off. A related note explains why MCP servers stop loading when an administrator adds managed-mcp.json during a session: it may apply at the next check, and open sessions should be restarted for it to apply in full.
Background Session and Gateway Fixes
One fix has direct operational weight. Background sessions that lost the LLM gateway exported by the shell, after a crash, after a reopen from another folder, or when the background service lacks it, now stop before any model request instead of sending the request somewhere unintended. That is the correct failure shape for a credential and routing problem: stop early and visibly, rather than fall back to a different gateway.
The rest of the long fix list covers session integrity in narrower cases. Resumed sessions no longer lose recent turns after a crash when the previous turn ended with an empty reply. Rules added in /permissions and folders added with /add-dir no longer look saved when the settings file could not be written; the terminal now warns and names the file. Settings files with values nested thousands of levels deep no longer crash the client; values past 64 levels are dropped with a warning. Each fix is small, and together they describe a client hardening its local state handling, which fits the pattern of the two releases before this one.
Limits and Unconfirmed Points
- Protected folder list not published: the release notes say some sensitive home folders are blocked for sandbox writes by default, without listing them. The full list is unconfirmed.
- Policy loading window not measured: how often sessions actually start before organization policy loads, and for how long, is not stated in the release notes.
- Code Mode still experimental: no stable release date or graduation criteria are given in the v2.1.326 notes.
- Fix list is selective here: the full v2.1.326 changelog contains a long list of additional fixes across sign-in, MCP, Remote Control and rendering. This article covers the entries that change mode, sandbox, permission or session outcomes.
FAQ
What is the main change in Claude Code v2.1.326?
Code Mode can now be turned on while agent teams are enabled. If you already turned Code Mode on, sessions with teams enabled now start in Code Mode.
How does the new auto mode startup default work?
Terminal and VS Code sessions with no mode set now start in auto mode, not Manual mode, when the organization policy has not loaded. Once settings load, a server-managed defaultMode can apply, or Manual if settings fail with no stored copy.
What changed in sandbox writes in v2.1.326?
Sandboxed commands on macOS, Linux and WSL no longer write to some sensitive home folders by default. Some folders can be allowed with sandbox.filesystem.allowWrite in user or managed settings. The full list of protected folders is not in the release notes.
Is Code Mode still experimental in v2.1.326?
Yes. The release expands where Code Mode can run, including agent teams, but the notes do not announce a move to a stable feature or give a date for one.
What should teams check after updating to v2.1.326?
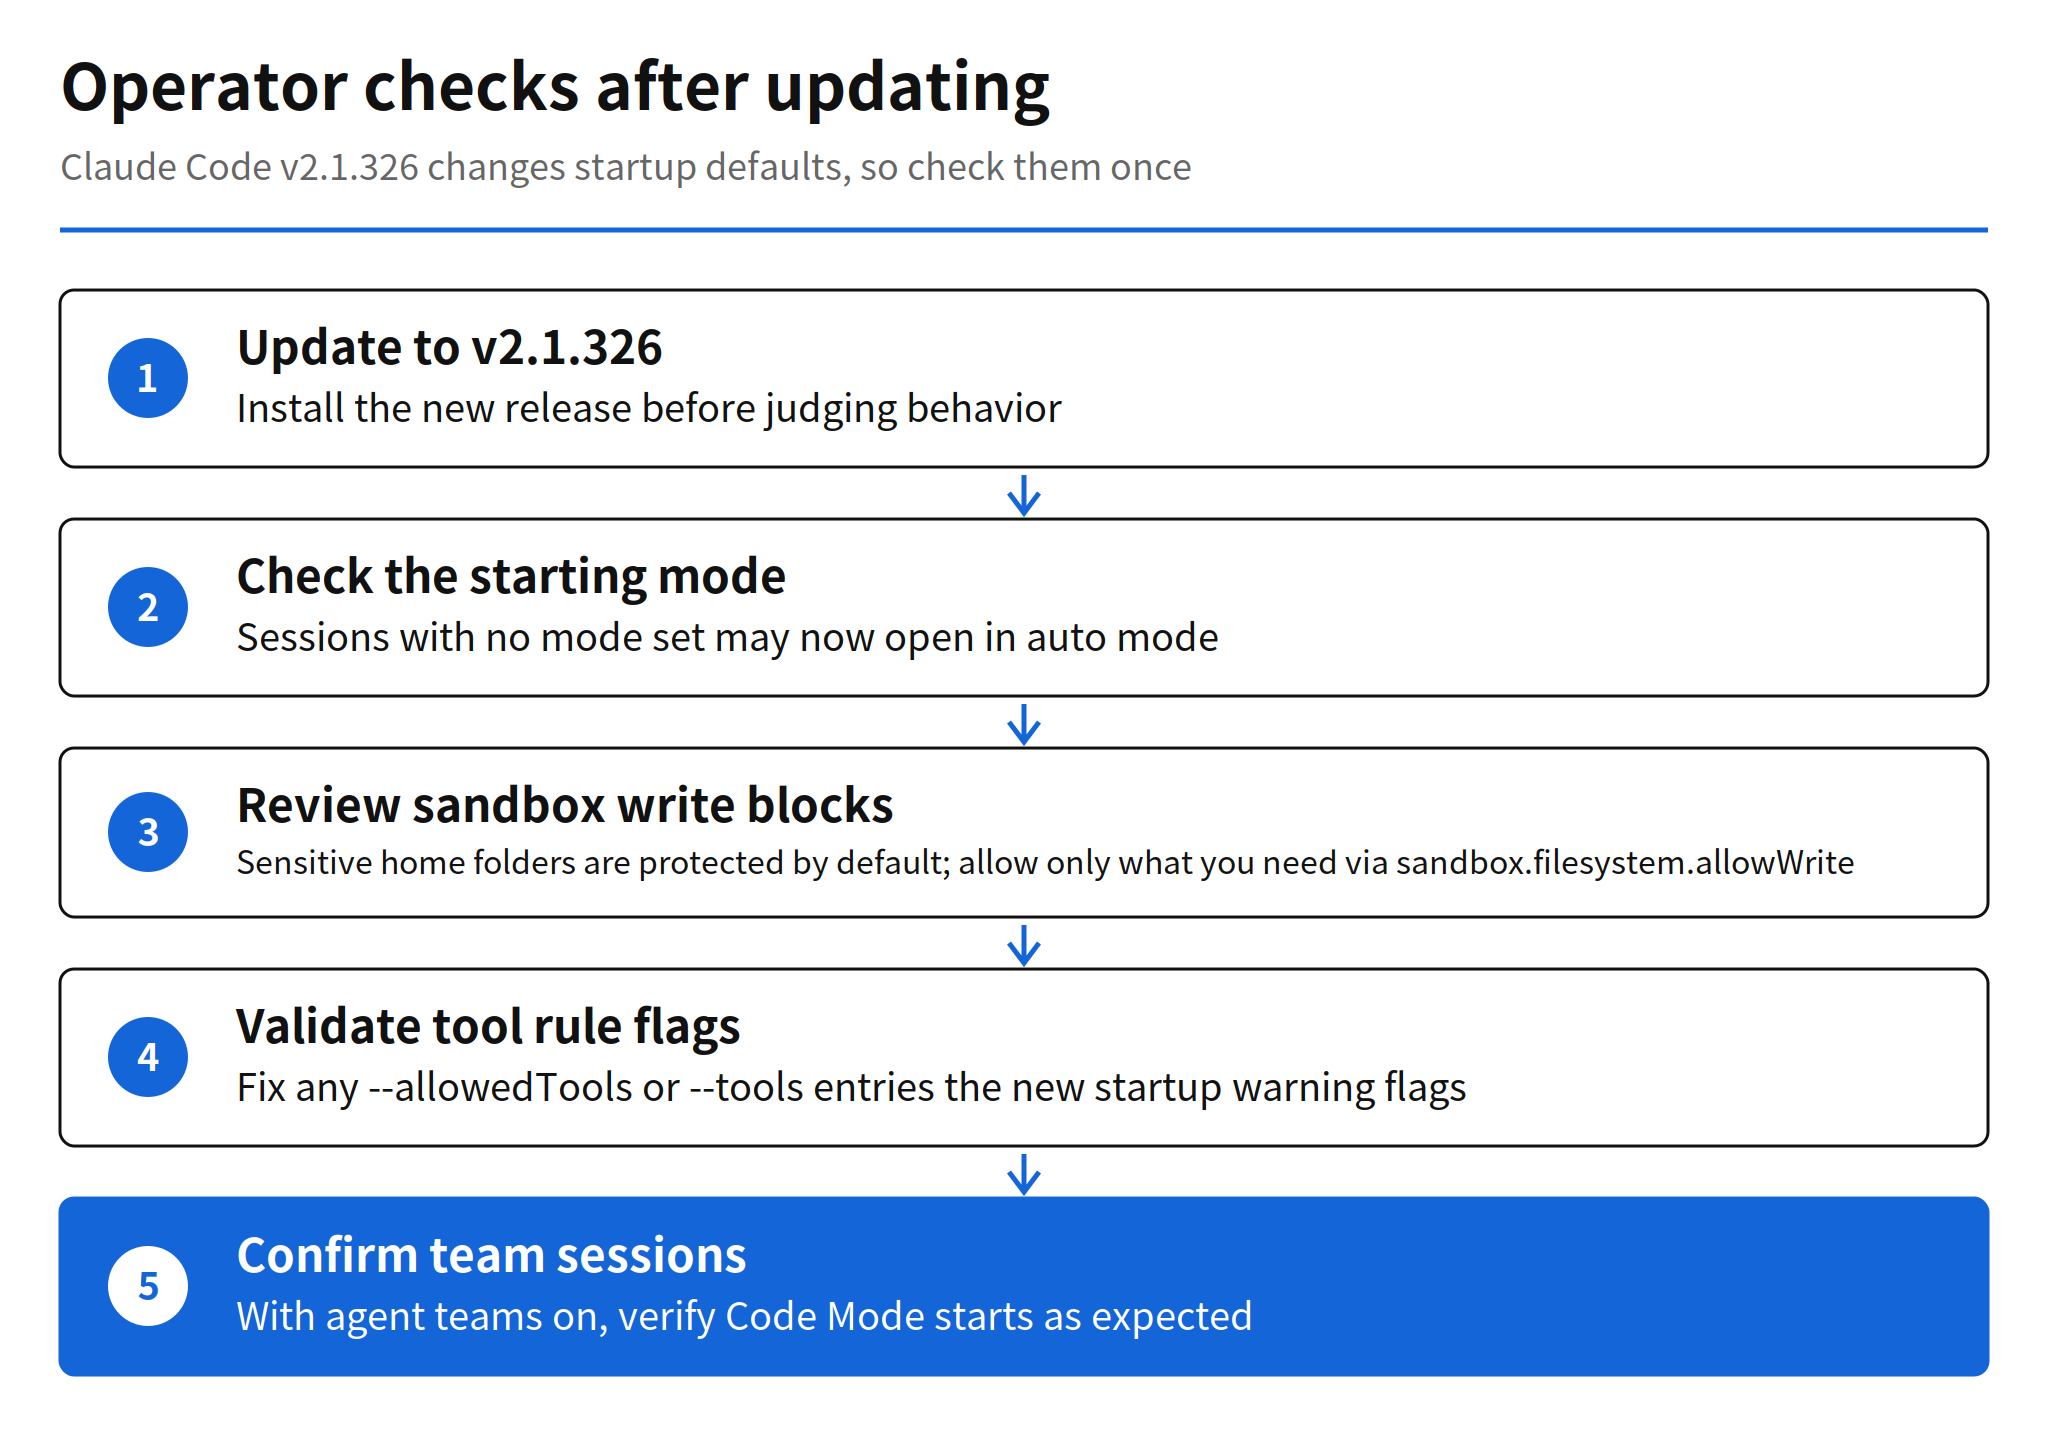
Check the starting mode of a fresh session, review any sandbox write blocks against needed folders, and fix any tool rule flags that trigger the new startup warning for incomplete rules.
Related Reading
- Claude Code v2.1.325: Sandbox Permissions and Security, the previous release in this series, which made sandboxed Bash follow the normal permission flow
- Claude Code v2.1.323 Release: Code Mode and 1M Context, the release that introduced the Code Mode now extended to agent teams