Claude Code v2.1.325: Sandbox Permissions and Security
Anthropic released Claude Code v2.1.325 on November 13, 2026. The npm package was published at 20:07 UTC and the GitHub release followed at 20:40 UTC. This is a hardening release, not a feature release. Sandboxed Bash commands now follow the normal permission flow by default, a security issue in zstd response decoding is fixed, and a gap that let some compound Bash commands run without asking is closed.
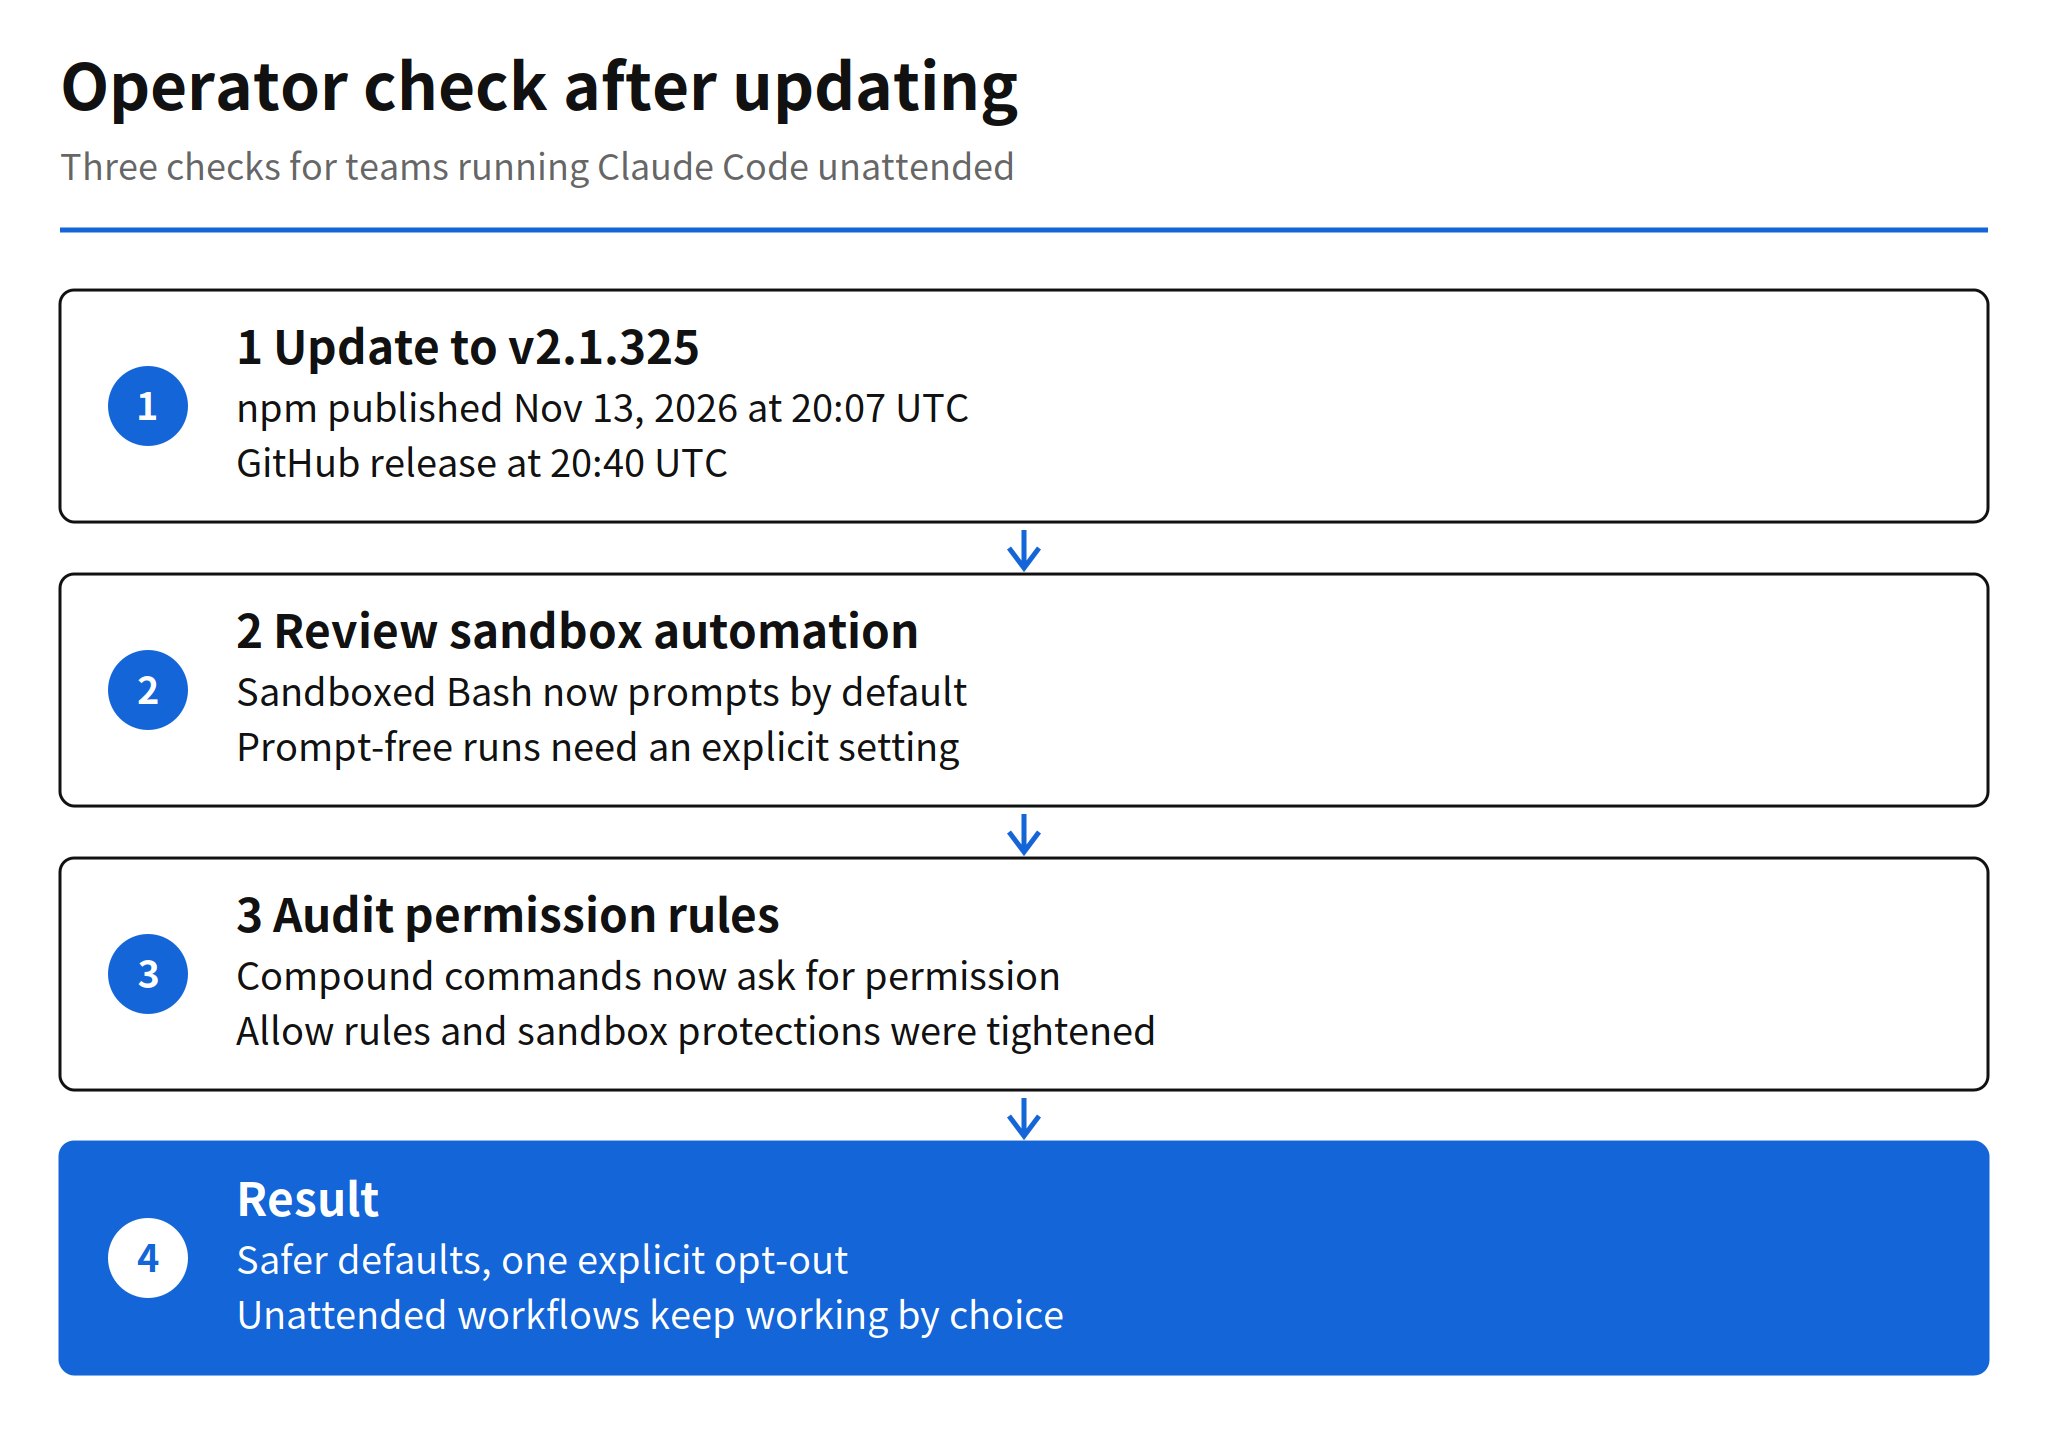
The default change is the part that will reach working setups first. Until now, a command inside the sandbox could run without a prompt on the assumption that the sandbox itself was the guardrail. From v2.1.325, the sandbox and the permission prompt are separate checks, and both apply unless an operator opts out in writing. Teams that run Claude Code unattended need to make that opt-out explicit, or their next session will stop at prompts nobody is watching.
Sandboxed Bash Permission Default
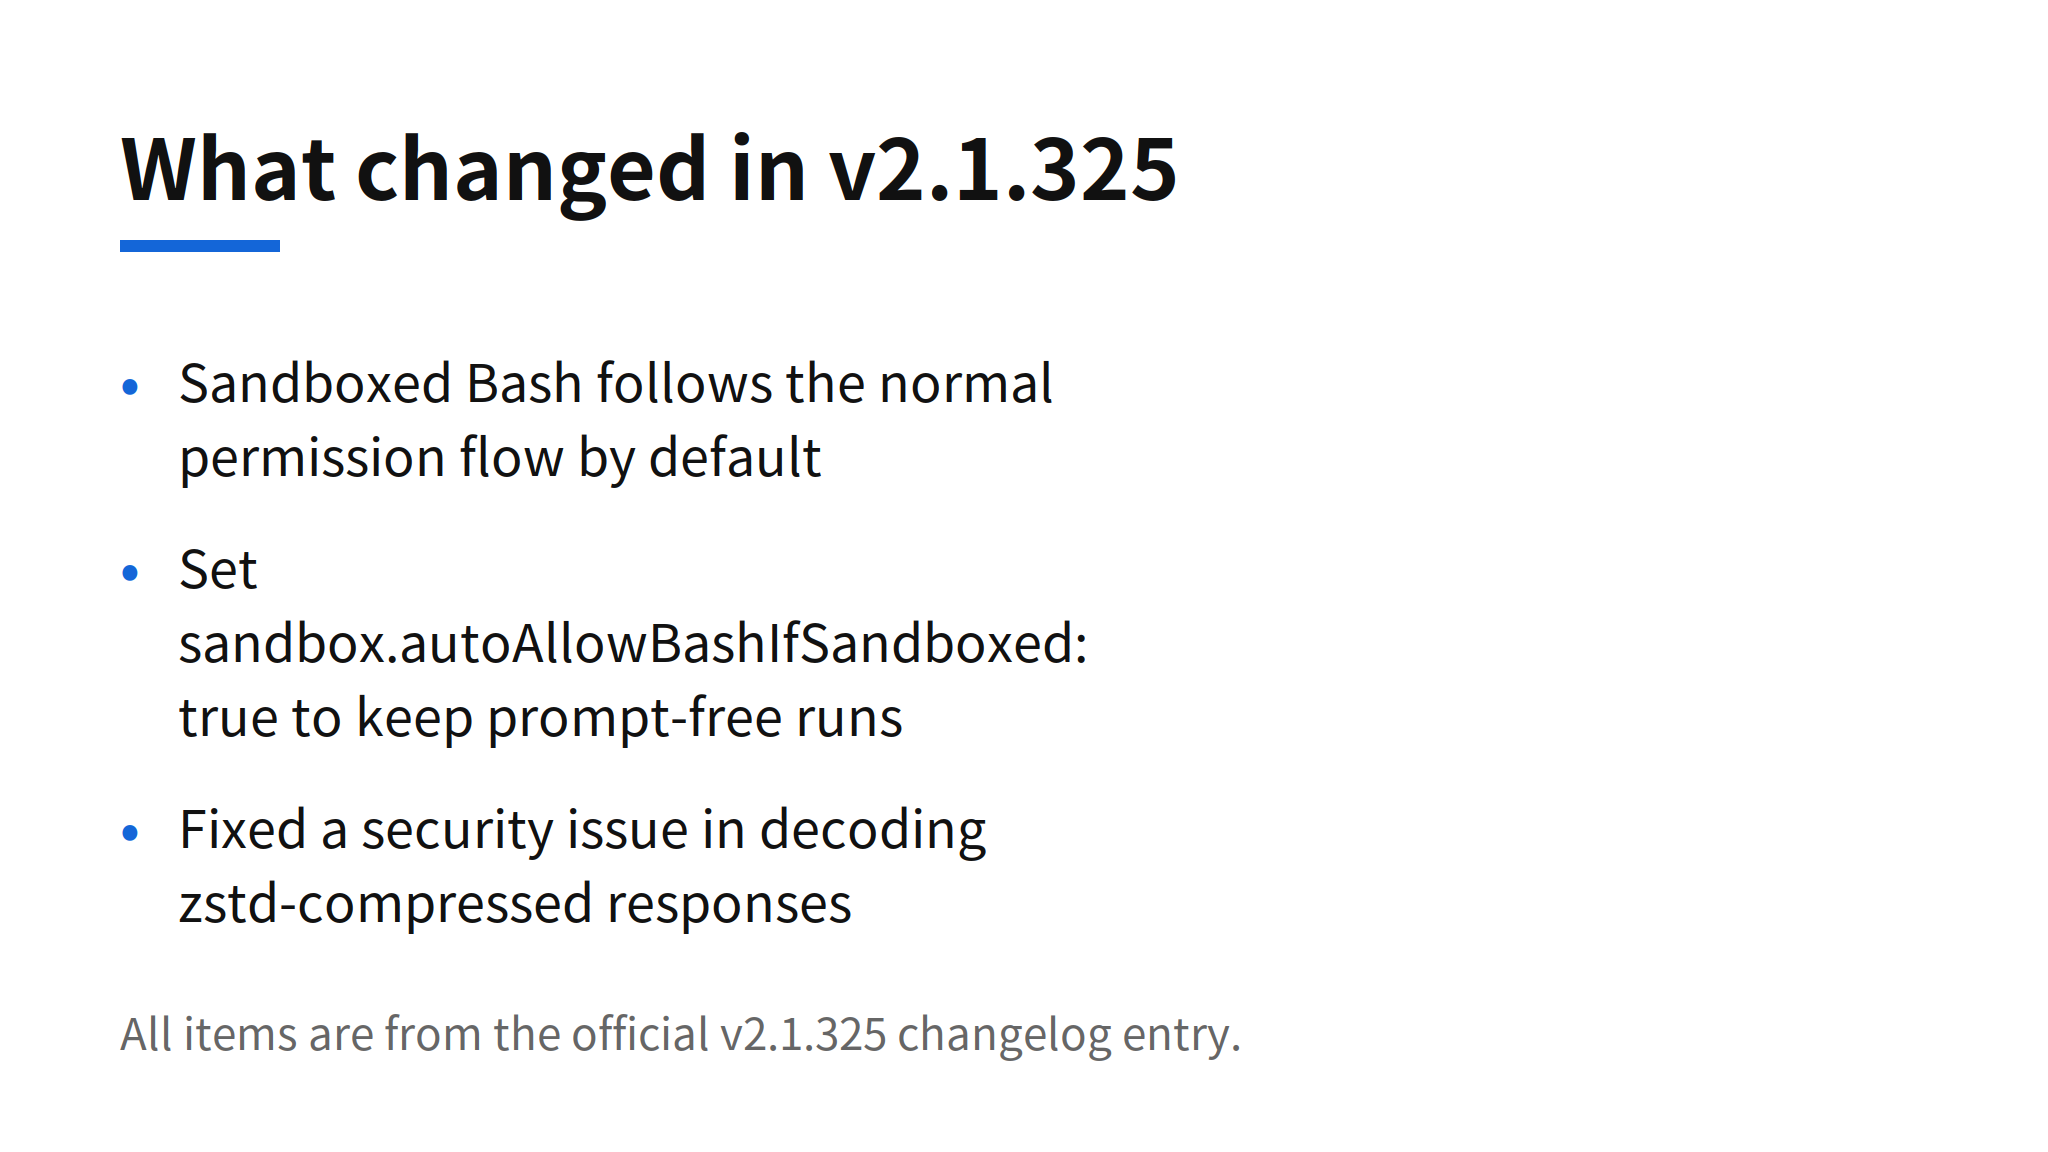
The changelog states the new default in one line: sandboxed Bash commands follow the normal permission flow by default, and setting sandbox.autoAllowBashIfSandboxed: true keeps the old prompt-free behavior. A second line covers managed deployments. When managed settings turn the sandbox on, the prompt-free setting has to sit in the highest ranking managed source, not in a local file that a managed policy can override.
That pairing is the design tell. Anthropic is not removing the unattended path, it is moving it from an implicit side effect of the sandbox to a named setting that an operator or an admin has chosen. For a personal setup, the cost is one line of configuration. For a team, the setting becomes part of the policy record, which is where a decision about running shell commands without prompts belonged in the first place.
The rest of the sandbox entries in this release point the same way. The sandbox now refuses writes to .claude settings, skills, agents, commands and hooks in added directories, as it already did in the launch folder. Programs the sandbox starts for its own use, such as its network bridge, run without Claude Code sign-in tokens and API keys in their environment. A case where the Bash sandbox could switch off during a session is fixed, and so is a case where sandboxed commands could read file checkpoint copies under the config directory. Each item is narrow. Together they describe a sandbox being treated as a boundary that has to hold on its own, not as a reason to skip the other checks.
My read: this is the correct direction, and it will still break quiet automation in the short term. Any wrapper, cron job or background agent that assumed sandboxed commands never prompt will hang at the first prompt after updating. The fix is cheap, but it has to be applied before the update, not discovered from a stalled session the next morning.
Zstd Security Fix and Permission Gaps
The first line of the v2.1.325 changelog is the security fix: a security issue in how zstd-compressed responses are decoded. Anthropic gives no vulnerability identifier, no severity rating and no affected version range in the changelog entry. That absence is worth stating plainly, because it limits what a reader can do with the information. There is no way to check exposure from the changelog alone. The practical response is simply to update, since the fixed version is the current one.
The permission fixes are described in more detail. A gap in Bash permission checks let some compound commands run without asking, and those commands now ask. A related fix covers a case where a Bash allow rule could run a different program than the one it names. Deny and ask rules also gained coverage in places they missed: relative rules such as Read(./.env) now still apply after a cd into added directories, rules for plugin MCP servers match across letter case, and deny rules apply again to approvals that arrive after a restart in self-hosted runner and remote-control sessions.
Read together, these entries are about the same failure shape. A permission system fails quietly when a command is parsed differently by the checker and by the shell, or when a rule stops applying after the working directory, the session or the process changes. Compound commands are the classic case, because one string can contain several programs. Closing that gap matters more for daily safety than the headline zstd fix, simply because it sits on a path every session uses.
Subagent, Gateway and Session Fixes
Two subagent fixes correct model handling. When the model setting is opusplan or haiku, subagents with their own model were being moved to the plan mode model, and that no longer happens. Separately, a subagent on a different model now sizes file reads and MCP results with its own model in mind, rather than the main session model. Both fixes protect a common pattern, a cheaper or specialized subagent doing bounded work, from silently inheriting the wrong model assumptions.
Session reliability also improved in ways operators will notice only when something goes wrong. Sessions on many third-party gateways and on Foundry stopped with a context length error on every turn instead of compacting, and that is fixed. Recent turns sometimes went missing when a session was resumed after Claude Code stopped without a clean exit, and that is fixed as well. When an organization policy blocks a request, the error now carries a line explaining how to continue, either by running /rewind and changing the message, or by running /clear.
Code Mode, introduced one release earlier in v2.1.323, receives follow-up repairs rather than new capability. Scripts in Code Mode no longer ignore a worktree entered with EnterWorktree, words typed with a Yes at a permission dialog now reach Claude in Code Mode, and resuming a session that ended during a Code Mode script no longer starts work by itself. That last fix matches the theme of the release: an agent resuming should wait for instruction, not improvise momentum.
Limits and Unconfirmed Points
- Zstd detail not published: the changelog confirms a security issue in decoding zstd-compressed responses and nothing more. Impact range and severity are not stated, so this article does not estimate them.
- No adoption data for the sandbox opt-out: how many setups rely on prompt-free sandboxed execution is not published. The breakage risk for unattended workflows is a direct reading of the new default, not a measured count.
- v2.1.324 difference unconfirmed: npm shows a 2.1.324 publish on November 13, 2026 at 18:42 UTC, but the changelog has no 2.1.324 entry. What changed between 2.1.324 and 2.1.325 is not confirmed here.
- Fix list is selective here: the full v2.1.325 changelog contains a long list of additional fixes across sign-in, MCP, rendering and platform behavior. This article covers the entries that change security, permission or session outcomes.
FAQ
What is the main change in Claude Code v2.1.325?
Sandboxed Bash commands now follow the normal permission flow by default. To keep running them without prompts, set sandbox.autoAllowBashIfSandboxed: true. For managed settings that turn the sandbox on, the setting belongs in the highest ranking managed source.
What security fix leads the v2.1.325 changelog?
Anthropic fixed a security issue in how zstd-compressed responses are decoded. The changelog gives no vulnerability identifier, affected range, or further detail.
What permission gap was closed in v2.1.325?
A gap in Bash permission checks let some compound commands run without asking. Those commands now ask for permission. The release also fixes cases where an allow rule could run a different program than the one it names.
What happened to v2.1.324?
Version 2.1.324 has an npm publish record dated November 13, 2026, but the changelog has no 2.1.324 entry. The difference between 2.1.324 and 2.1.325 is not confirmed in the sources used for this article.
Should unattended Claude Code setups update to v2.1.325?
Yes, but review the sandbox setting first. After the update, sandboxed commands will prompt unless sandbox.autoAllowBashIfSandboxed is set to true, so unattended workflows need that choice made explicitly in configuration.
Related Reading
- Claude Code v2.1.323 Release: Code Mode and 1M Context, the previous release in this series, which introduced the Code Mode that v2.1.325 now repairs